Talweg
· Talweg Team · Cybersecurity · 5 min read
Beyond Log Enrichment: Next-Generation SIEMs Built on FlinkFlow
Explore how real-time stream processing with FlinkFlow is shifting Security Information and Event Management (SIEM) systems from reactive historical analysis to proactive, instant threat mitigation.
Introduction
For over a decade, the Security Information and Event Management (SIEM) landscape has been dominated by batch-oriented platforms. These legacy systems ingest massive amounts of log data into central repositories, allowing analysts to query historical data and hunt for threats after the fact.
However, modern cyber threats operate at machine speed. The delay inherent in indexing, storing, and periodically querying logs means that by the time an alert fires, the damage is often already done. The cost of running these platforms has skyrocketed alongside data volumes, leading to significant infrastructure costs and debilitating “alert fatigue” for security analysts.
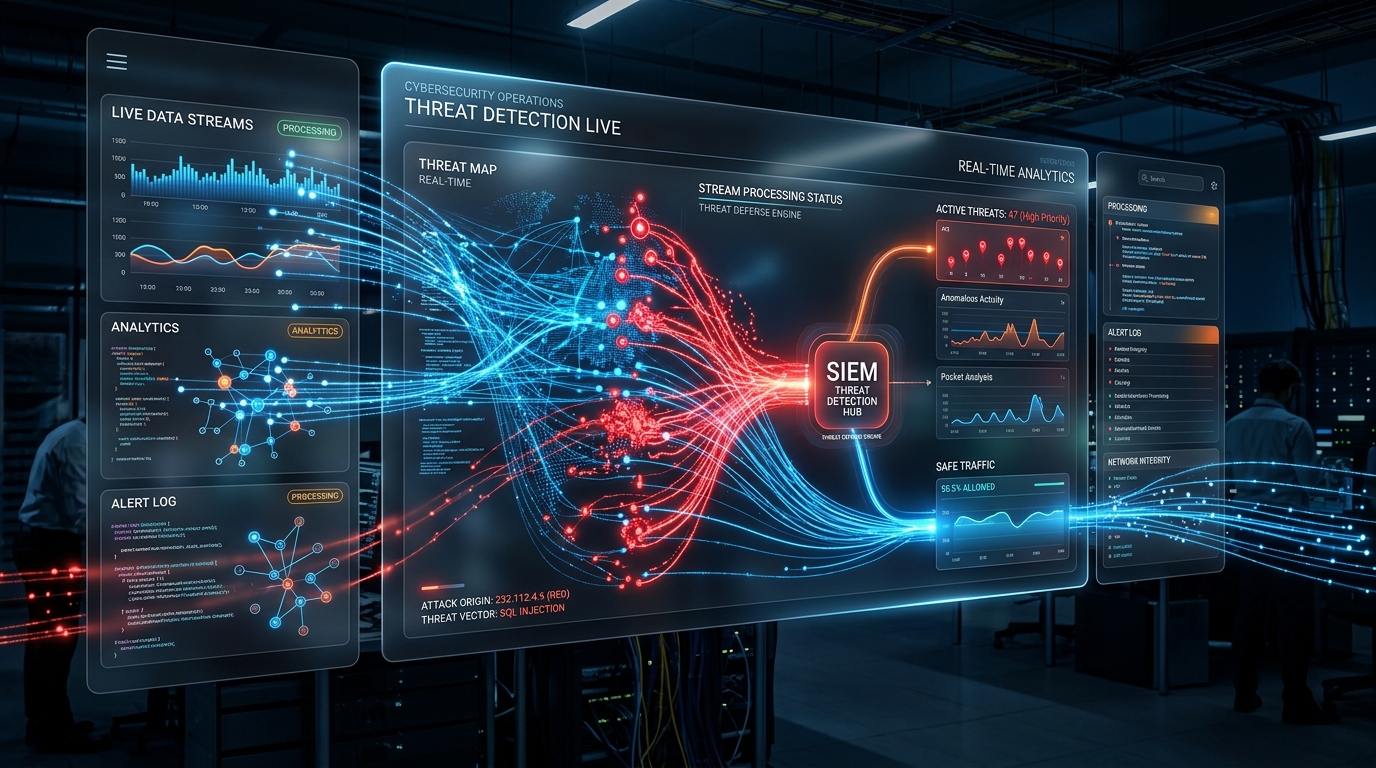
Real-time stream processing is shifting the paradigm. By moving security rules to the stream itself, next-generation SIEMs built on declarative frameworks like FlinkFlow are shifting from reactive historical analysis to proactive, instant threat mitigation.
The First Step: Real-Time Log Enrichment (A Quick Recap)
One of the most common initial use cases for streaming in cybersecurity is real-time log enrichment. When a raw event (such as a firewall connection log or a user authentication attempt) hits the ingestion pipeline, stream processors can instantly join this data with contextual information.
For instance, appending geolocation data to an IP address, or checking a threat intelligence feed to see if an IP is known to be malicious, provides immediate context to raw events.
While crucial, simple enrichment is no longer sufficient on its own. Attackers often use valid credentials and legitimate infrastructure, meaning individual enriched events might not look suspicious in isolation. Detecting these threats requires analyzing sequences of events over time.
Moving “Beyond Enrichment”: Complex Event Processing (CEP)
This is where Complex Event Processing (CEP) enters the picture. CEP allows security teams to identify meaningful patterns and relationships across multiple streams of data in real time.
Instead of writing a query to find all failed logins from yesterday, you can define a pattern in FlinkFlow such as: “Identify 5 failed login attempts followed by a successful login from a new IP address within a 2-minute window.”
Crucially, FlinkFlow evaluates these complex patterns in-memory, on the fly. It doesn’t need to write the events to a database and query them back. This dramatically reduces the time to detection (TTD) from minutes or hours down to milliseconds.
Stateful Threat Detection with FlinkFlow
The core missing piece in many legacy security pipelines is state. Modern cybersecurity heavily relies on User and Entity Behavior Analytics (UEBA), which requires understanding what is “normal” for a specific user or system and immediately flagging deviations.
FlinkFlow manages distributed state seamlessly. It can maintain a running profile for millions of distinct entities without relying on external lookups to slow databases.
For example, FlinkFlow can continuously track the average outbound bandwidth used by every single workstation on your network. If a workstation suddenly spikes to 50x its normal outbound bandwidth (a classic indicator of data exfiltration), FlinkFlow, holding that baseline state, detects the anomaly and triggers an alert instantly.
Declarative Security Rules: Flink SQL in Action
Maintaining hundreds or thousands of complex, stateful detection rules written in low-level Java or Scala is a nightmare for security engineering teams.
FlinkFlow abstracts away this complexity, allowing analysts to author streaming detection rules using familiar declarative SQL. This democratizes threat detection, empowering analysts to write and deploy rules without needing to become distributed systems engineers.
Here is a simplified example of how an analyst might use Flink SQL within FlinkFlow to detect a potential brute-force attack or credential stuffing:
name: "Brute Force Detection Pipeline"
parallelism: 1

steps:
  - type: sql
    name: detect-brute-force
    inputs: [authentication_logs]
    properties:
      schema.authentication_logs.user_id: "string"
      schema.authentication_logs.source_ip: "string"
      schema.authentication_logs.status: "string"
      schema.authentication_logs.event_time: "timestamp(3)"
      query: |
        SELECT
            user_id,
            source_ip,
            COUNT(*) as failed_attempts,
            TUMBLE_START(event_time, INTERVAL '1' MINUTE) as window_start
        FROM authentication_logs
        WHERE status = 'FAILED'
        GROUP BY
            TUMBLE(event_time, INTERVAL '1' MINUTE),
            user_id,
            source_ip
        HAVING COUNT(*) > 10;
This query continuously evaluates a sliding 1-minute window, instantly outputting a record the moment an IP address fails more than 10 logins for a specific user within that timeframe.
Automated Remediation
Detecting a threat in milliseconds is only half the battle. What happens after the alert fires?
Because FlinkFlow operates in real-time and integrates seamlessly with enterprise ecosystems, it can be the engine for automated remediation. Instead of just sending an alert to a dashboard where an analyst might see it 20 minutes later, FlinkFlow can instantly trigger a webhook or publish a message to a Kafka topic that an orchestration system consumes to:
- Instantly add a malicious IP address to a firewall blocklist.
- Automatically revoke a user’s session tokens across the application.
- Isolate a compromised workstation from the rest of the network.
This closes the loop, turning detection into immediate, automated action.
Conclusion
Building a SIEM or security analytics platform on FlinkFlow fundamentally changes the economics and efficacy of threat detection.
By analyzing data as it streams in, evaluating complex stateful patterns in-memory, and enabling analysts to write rules in declarative SQL, organizations can achieve lower latency and a proactive security posture. Furthermore, by filtering out or aggregating non-essential data before it hits expensive cold storage, organizations can significantly rein in the runaway costs of log retention.
The future of cybersecurity is streaming, and FlinkFlow provides the robust, stateful, and developer-friendly foundation required to build it.